The scope is displayed first
Target and subdomain setting, requests per second, the four HTTP methods, the excluded paths, and the fixed source addresses the traffic comes from.
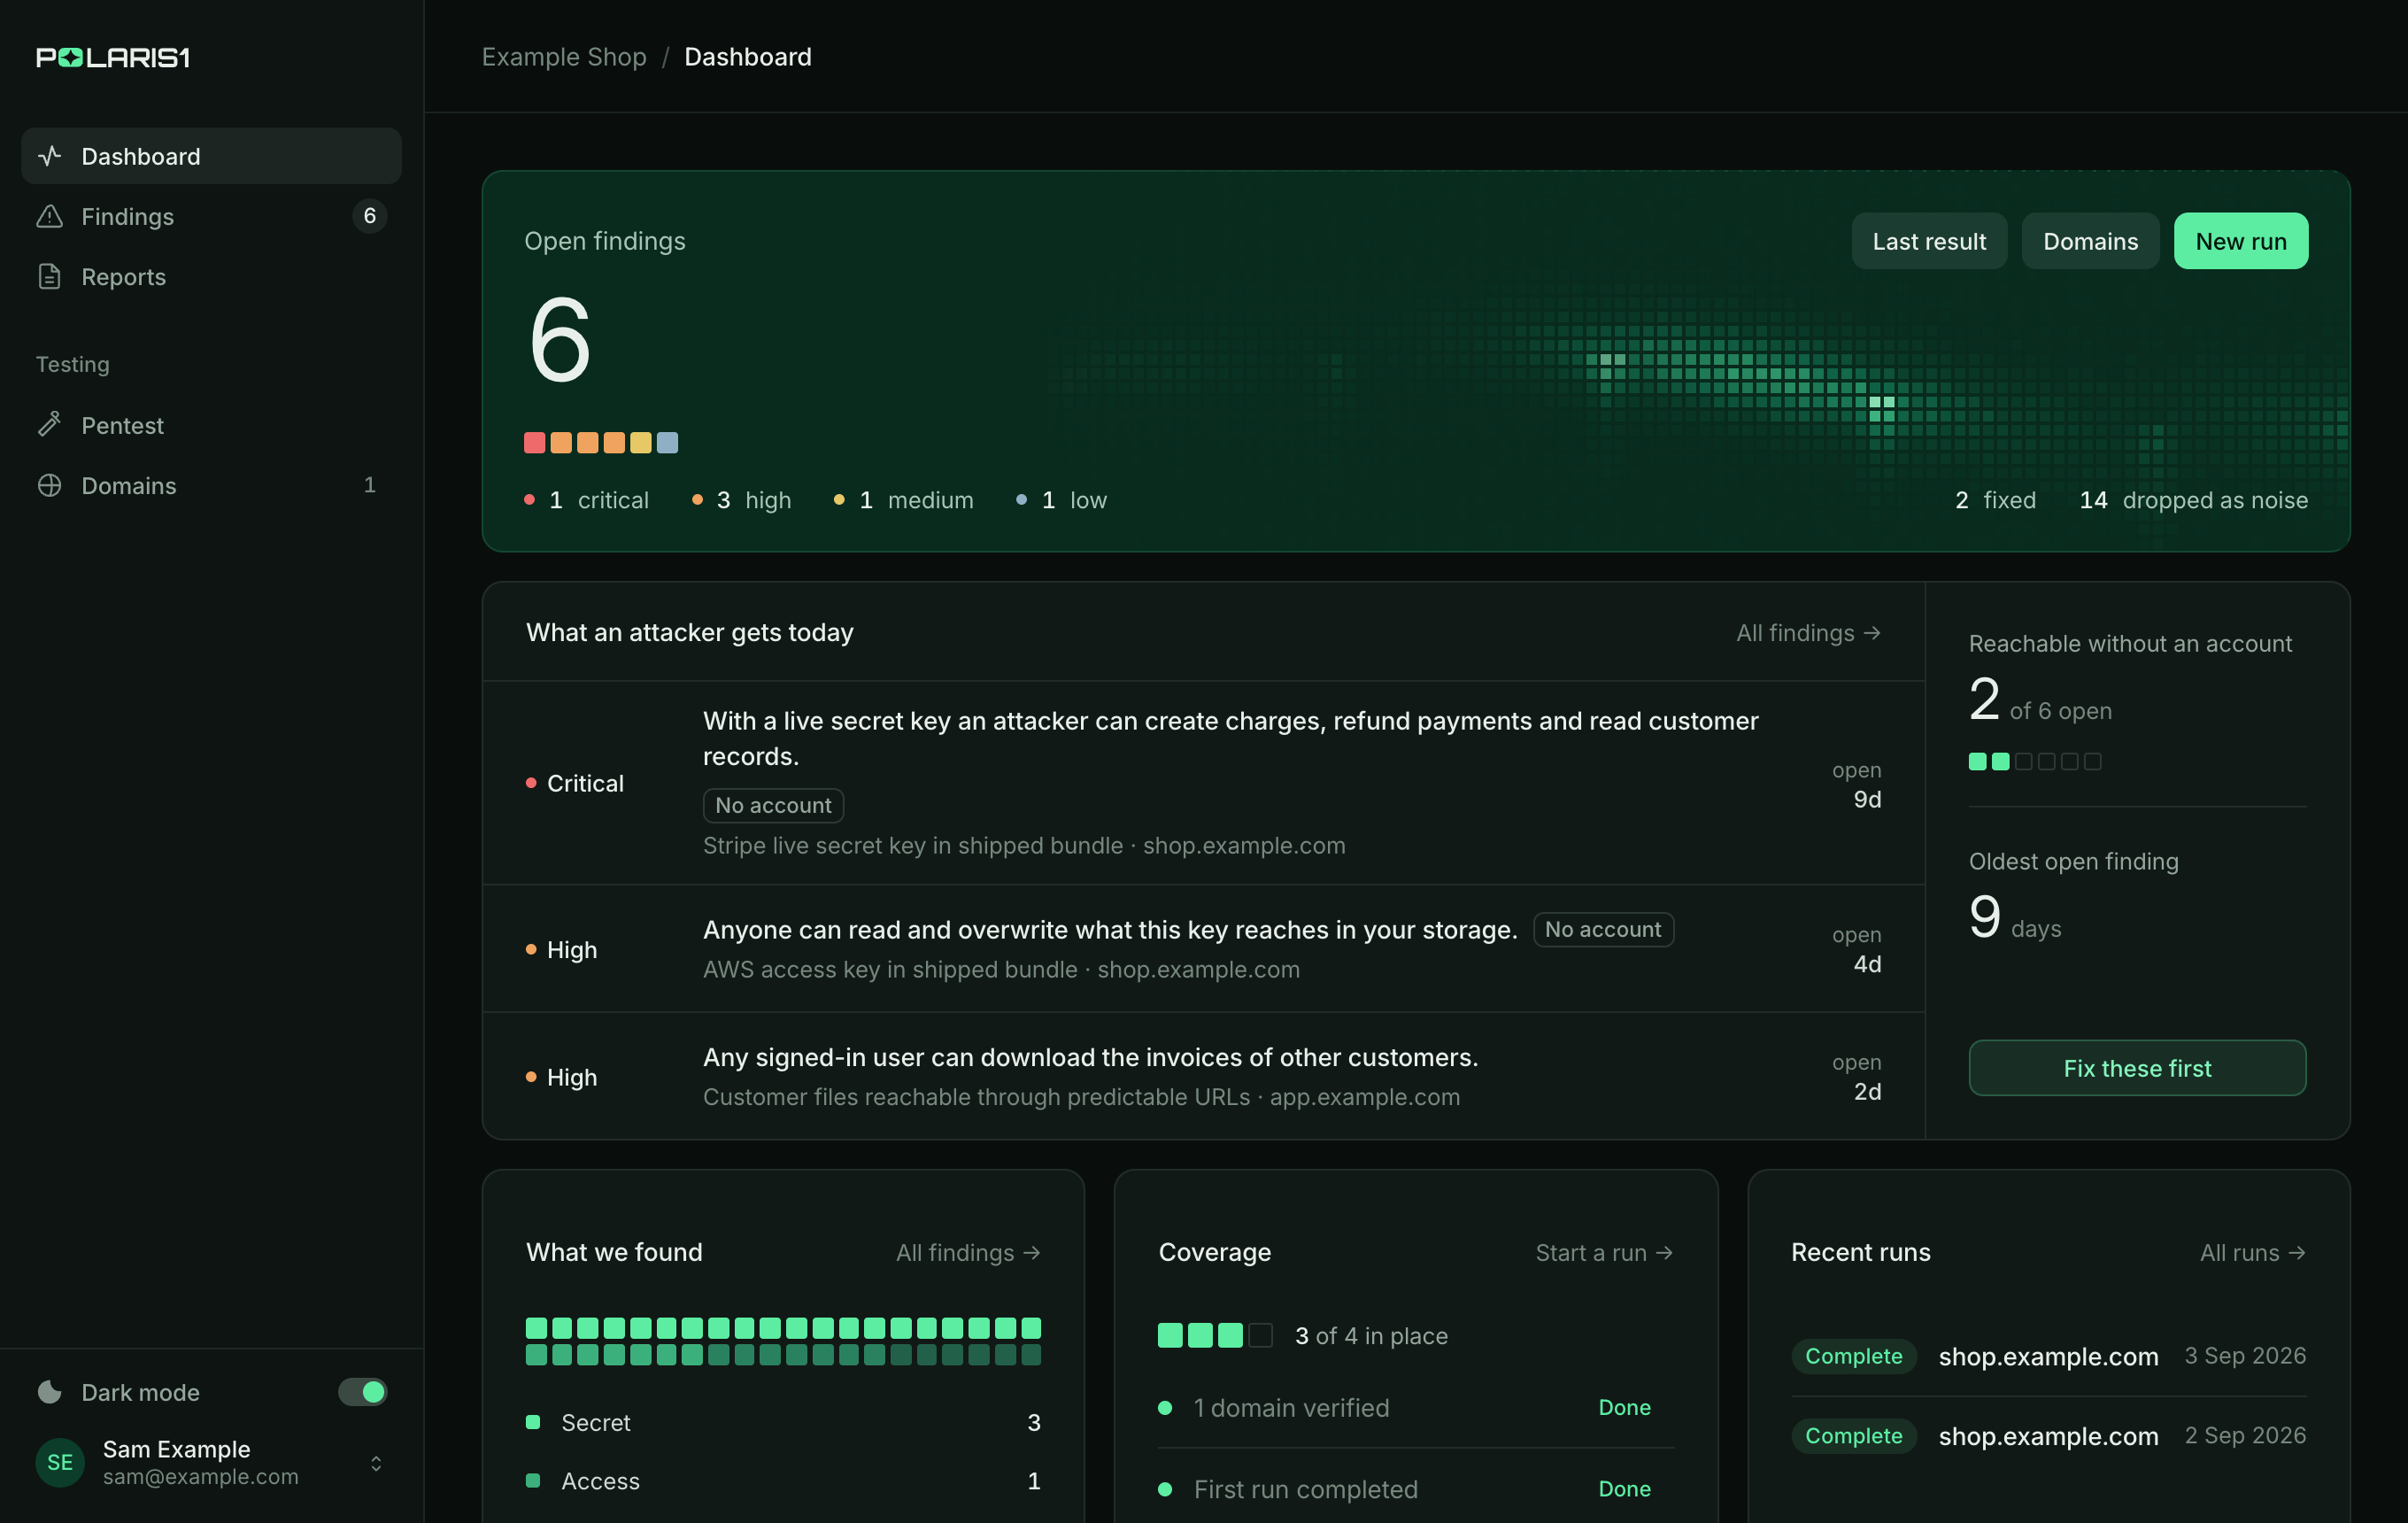
A full external pentest of everything you expose. Every finding comes with where it sits, the proof and the fix — and if nothing serious turns up, no invoice.

Domain
That is the whole form. Everything else is optional.
Start testAdd this TXT record
Checked before the first run and re-checked before every later one.
Two independent resolvers
Remove the record and testing stops.
Phases
You set the pace
A running test is stopped with a single call and ends within seconds.
for the count, always.
Nothing serious proven? The run is waived.
PLS-1042 · proven 2×
Stripe secret key shipped in your JS bundle
41 candidates did not survive
/assets/index-4f2a.js, line 2,481. Mapped through your sourcemap to src/lib/payments.ts, line 12 — if you ship one.Re-test
It runs the same two passes against the same place, and either the finding closes or it does not.
You name the target. Nothing else. No agent to install, no code access, no credentials. A domain is enough — everything happens from the outside, the way a stranger sees you. What the product is
One DNS record, checked twice. We will not touch a host you have not proven. Two independent resolvers have to agree — a single one can be stale or redirected, and ownership is the only ticket in. Limits and controls
You watch it happen. And you can stop it. Phases report live, and you decide how hard we push your production system. What we have not built says skipped instead of showing a progress bar for work nobody did — an invented number would be worse than an honest gap. How a run works
The count is free. Always. How many and how bad costs nothing. If nothing serious was proven, the run is waived and you are never charged — that is the whole pricing model in one sentence. See pricing
The name, the place, the proof, the fix. Every finding was reproduced with different parameters before it reached your list. 41 candidates did not survive that step. This is why the report has three lines and not 1,428. Four reports
We tell you what to change and where. A suggestion, not a pull request. We never write to your code and never hold credentials — the whole test runs read-only from the outside. What you do with it is your call. How the re-test works
Four reports the same day — one to forward, one for your developers.
candidatesnot reproducible
41
did not survive the second pass. Not downgraded to informational, not moved to an appendix.
PLS-1043proven 2×
Customer files reachable through predictable URLs
PLS-1044proven 2×
Reset link still works after the password changed
PLS-1042closed
Stripe secret key shipped in your JS bundle
One to forward, one for your developers, two for your audit. Dated, as PDF, and you can export them as often as you like.
Target and subdomain setting, requests per second, the four HTTP methods, the excluded paths, and the fixed source addresses the traffic comes from.
The same ciphertext decrypted under a different account yields nothing — a property of the encryption, not of an access rule.
Unredacted evidence opens through a link valid for minutes. Secrets are redacted before storage.
Evidence and reports live on machines in Frankfurt, with keys in eu-central-1. Every processor is named, and a data processing agreement is available.
Privacy policy, processorsBy a job that runs on a schedule and can be checked, not by a storage provider’s retention setting.
How long we keep thingsAn NDA is the default, and no client is named anywhere without written permission.
How we workTell us and we will credit you. Disclosure mail is answered first, before anything else.
Report a vulnerability| Aspect | Booked pentest | Plaris1 |
|---|---|---|
| Price | $8,000 – $30,000 | €199 |
| Testing | 3 – 10 days | Minutes |
| Report | 3 – 7 days after | Immediately |
| First contact to report | 4 – 8 weeks | Same day |
| Nothing serious found | Full fee | No invoice |
| Retest after the fix | Usually billed again | Free, 14 days |
A pentest is a snapshot of one day. You ship every week, and the report starts ageing the moment it is written. This takes minutes — run it again the day you ship, and again after the fix, free, for fourteen days.
A key can do exactly two things — start a run and read the counts.
Add a domain, prove it is yours with one DNS record, start the run. When it ends you see how many findings there are and how serious — by severity, as a count.
No card, no commitment
Titles, locations, proof and fixes stay closed until you unlock them. You decide with the count already in front of you, so you are never paying to find out whether it was worth paying.
Only if something critical or high was proven
Mark what you fixed, push it, and run the test again against those findings. One re-test, within fourteen days, at no cost — however many findings it covers.
Once per paid run
€199/ test
One application and its APIs, tested end to end. No card to start, no subscription, no minimum term.
Every test includes
Nothing critical or high proven — no invoice.
Several repositories, internal apps, SSO or a signed DPA? Talk to us
Something missing? Ask us directly — a person answers.
A leaked key is never one finding. It is your database, your storage and your payments in someone else’s hands — and nobody warns you first. The free check takes ten minutes and nothing from your team.